7 Best SOC 2-Compliant AI Customer Service Agents (2026)
A failed security review stalls the deal for weeks. Here are 7 SOC 2 compliant AI customer service agents that clear InfoSec, with real reports to prove it.
Summarize with AI
The deal got to yes. Your support manager ran the trial, the numbers looked good, the VP signed off on budget.
Then someone forwarded it to security, and the first email back asked for the actual attestation: which period it covered, who signed it. Everything stopped while you waited to find out whether the vendor even had one.
That's the moment I wrote this post for. "SOC 2 compliant" gets printed on every AI vendor's homepage. A security reviewer checks something harder: whether your customers' ticket data is safe the moment it hits an LLM, and whether the paperwork survives a real diligence pass.
Half the tools that say "SOC 2" mean "we started the audit" or "we're aligned with the framework". That gap is where deals slip.
You're probably here because one of these happened:
- InfoSec bounced a vendor mid-trial because its compliance badge turned out to be just an engagement letter, with no finished audit behind it.
- You're in a regulated vertical and need to know which vendors carry HIPAA for health data, ISO 27001, or PCI as well, beyond a vague "enterprise-grade" claim.
- You want AI answering tickets inside your helpdesk without opening a brand-new path for customer data to leak out to an LLM.
I've scored seven AI customer service agents against what a security review actually gates on, using what each vendor publishes and lets you verify, with the marketing set aside. One of them is ours (My AskAI), and I've held it to exactly the same bar, which is why we don't top the table.
A real proof point sits behind that: GiveCard, a fintech that runs prepaid cards and disbursements for benefit and aid programs, cleared My AskAI through its own security bar and now runs us at 95% resolution. A regulated money-mover doesn't put a vendor it can't verify on the front line.
What does "SOC 2-compliant AI customer support" actually require?
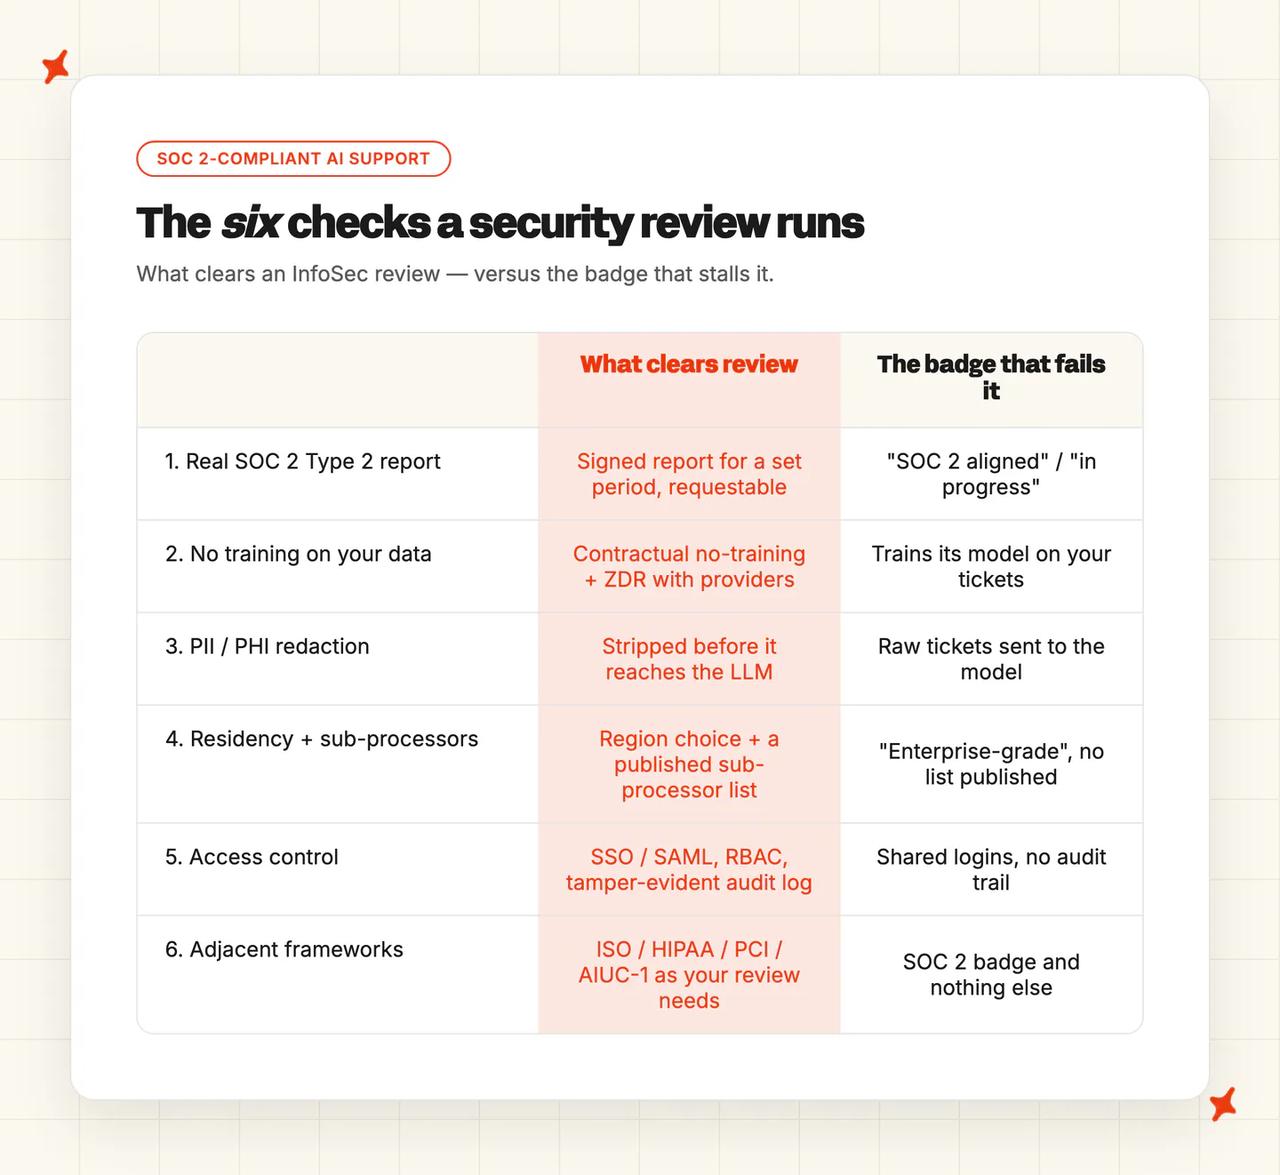
"SOC 2 compliant AI support" is six distinct things a security reviewer checks, and I score every vendor against all six. Most vendors have the logo and three of them.
The two the whole thing turns on are specific to AI, and a generic SOC 2 checklist walks straight past them: what happens to your customers' data once it reaches a language model, and whether you can verify any of the claims or are simply asked to take them on trust.
1. A real, current SOC 2 Type 2 report
"SOC 2 aligned", "in progress", "Type I", and a badge with nothing behind it all fail this test. A Type 2 attestation covers a period of operating effectiveness (for example April to October 2025), is signed by a named auditor, and is requestable under NDA, ideally self-serve from a live trust center running on Vanta, Secureframe or SafeBase. The gap between "we're SOC 2" (a badge) and "here is our Type 2 report for the last period" (an attestation) is the single most common place a review stalls.
2. No training on your data
This is the AI-specific risk a generic checklist misses. Customer tickets carry your customers' personal data, and when that goes to an LLM three questions decide the review: does the vendor train its own models on your data, do the third-party model providers (OpenAI, Anthropic) retain or train on it, and what's the retention window? What good looks like is contractual no-training, plus zero-data-retention (ZDR) agreements with the model providers, plus per-customer isolation.
3. PII / PHI redaction and data minimization
Sensitive data (names, cards, SSNs, health records) detected and stripped or masked before it reaches the LLM, and in the logs and transcripts afterwards. Minimizing what leaves your perimeter is what turns "we send tickets to OpenAI" from a review-blocker into a footnote.
4. Data residency and sub-processor transparency
Can you choose where data is hosted (US, EU, elsewhere), and does the vendor publish a current sub-processor list plus a DPA so your DPO can assess the whole chain? "Enterprise-grade security" with no published sub-processor list reads to a reviewer as a diligence red flag.
5. Access control
SSO / SAML, role-based access (RBAC), and a tamper-evident audit log of who accessed or changed what. Mid-market and up will not sign without SSO, and the audit log is what lets you answer "who saw this ticket" six months later.
6. Adjacent frameworks for your industry
GDPR and a DPA are table stakes. Beyond that, your review demands whatever your regulator does: ISO 27001 / 27701 for infosec and privacy management, HIPAA plus a BAA for health, PCI-DSS for payments, or the newer AI-specific standards like ISO 42001 and AIUC-1, the first cert built for AI agents. A vendor with SOC 2 and none of these is fine for a typical SaaS buyer and a hard no for a hospital.
A vendor with fewer than four of these six is just a chatbot with a badge. The two that trip most buyers are the first (a verifiable report you can pull) and the second (what actually happens to your data at the model).
How I scored these tools for SOC 2 and security readiness
I score every vendor on eight criteria: the six capabilities, plus setup-and-review-clearance speed (how fast and cleanly a tool passes InfoSec) and cost at typical volume (a predictable bill versus sales-gated or usage-shock pricing). Each is scored out of 10, for an Overall out of 80.
The equal-weight sum almost certainly isn't how your review weights these. A healthcare buyer should re-weight adjacent frameworks up; a lean SaaS team should push cost and review-speed to the front.
I marked strictly. A vendor that only "aligns" with SOC 2, shows an engagement letter with no report, or won't publish a sub-processor list gets marked down for it, with no benefit of the doubt, including for us.
The 7 SOC 2-compliant AI customer service tools: at a glance
| (scores out of 10) | My AskAI | Intercom Fin | Zendesk | Forethought | Ada | Decagon | eesel |
|---|---|---|---|---|---|---|---|
| Real SOC 2 Type 2 report | 10 | 10 | 10 | 9 | 10 | 10 | 3 |
| No training on your data | 10 | 6 | 6 | 8 | 9 | 9 | 9 |
| PII redaction / data-min | 4 | 5 | 8 | 9 | 8 | 8 | 7 |
| Residency + sub-processor transparency | 6 | 8 | 9 | 5 | 8 | 7 | 7 |
| Access control (SSO/RBAC/audit) | 6 | 9 | 9 | 7 | 9 | 9 | 5 |
| Adjacent frameworks | 3 | 10 | 10 | 8 | 8 | 9 | 3 |
| Setup & review-clearance speed | 10 | 6 | 5 | 3 | 4 | 3 | 7 |
| Cost at typical volume | 9 | 4 | 3 | 4 | 3 | 3 | 6 |
| Overall (/80) | 58 | 58 | 60 | 53 | 59 | 58 | 47 |
Same eight criteria, in plain words:
| My AskAI | Intercom Fin | Zendesk | Forethought | Ada | Decagon | eesel | |
|---|---|---|---|---|---|---|---|
| SOC 2 report | Certified; current Secureframe report | Type II, NDA report | Type II, NDA report | Type II, annual | Type II plus SOC 3 | Downloadable reports plus bridge letter | In-progress; engagement letter only |
| Training | Never trains any model | Trains own model, opt-out | Account models train on data | No shared-model training | No training; publishes ZDR | Zero-day retention, no training | Contractual no-training |
| Redaction | Isolation, no dedicated redaction | Native card masking only | ADPP add-on redaction | Default PII/PHI redaction | Built-in, configurable | Google DLP redaction | Strips PII before providers |
| Residency | Public sub-proc; residency undocumented | US/EU/AU; sub-proc gated | Selectable regions; public sub-proc | Residency undocumented; sub-proc gated | Contractual residency; public list | Published sub-proc; multi-region | EU on request; partial list |
| Access control | RBAC and audit; SSO undocumented | SAML SSO, RBAC | SSO, RBAC, audit | RBAC; SSO undetailed | RBAC, MFA, audit, FINRA | SSO, RBAC, tamper-proof audit | SSO Enterprise-gated; RBAC |
| Adjacent frameworks | GDPR only | ISO stack, AIUC-1, HIPAA | ISO, PCI L1, FedRAMP | ISO 27001, HIPAA, NIST | HIPAA, PCI AOC, AIUC-1 | ISO 27001, HIPAA, PCI | GDPR/CCPA; HIPAA gated |
| Review-clearance speed | Helpdesk-native, self-serve, fast | Self-serve but heavier footprint | Complex; add-ons stack | 30 to 90 day implementation | 8 to 16 week implementation | Sales-gated, enterprise-only | Self-serve on helpdesk |
| Cost | $0.10/ticket, transparent | Per-resolution $0.99 plus seats | Add-ons plus per-resolution | Opaque, sales-gated | Opaque, ≥300k bar | Opaque, enterprise-only | Tiered/PAYG, pay-twice |
Zendesk lands top on breadth: it holds the widest verified cert grid in the set, including PCI-DSS Level 1 and FedRAMP. Ada is a point behind on a well-documented public trust center, and Intercom Fin, Decagon and My AskAI sit level another point back, though they get there by opposite routes.
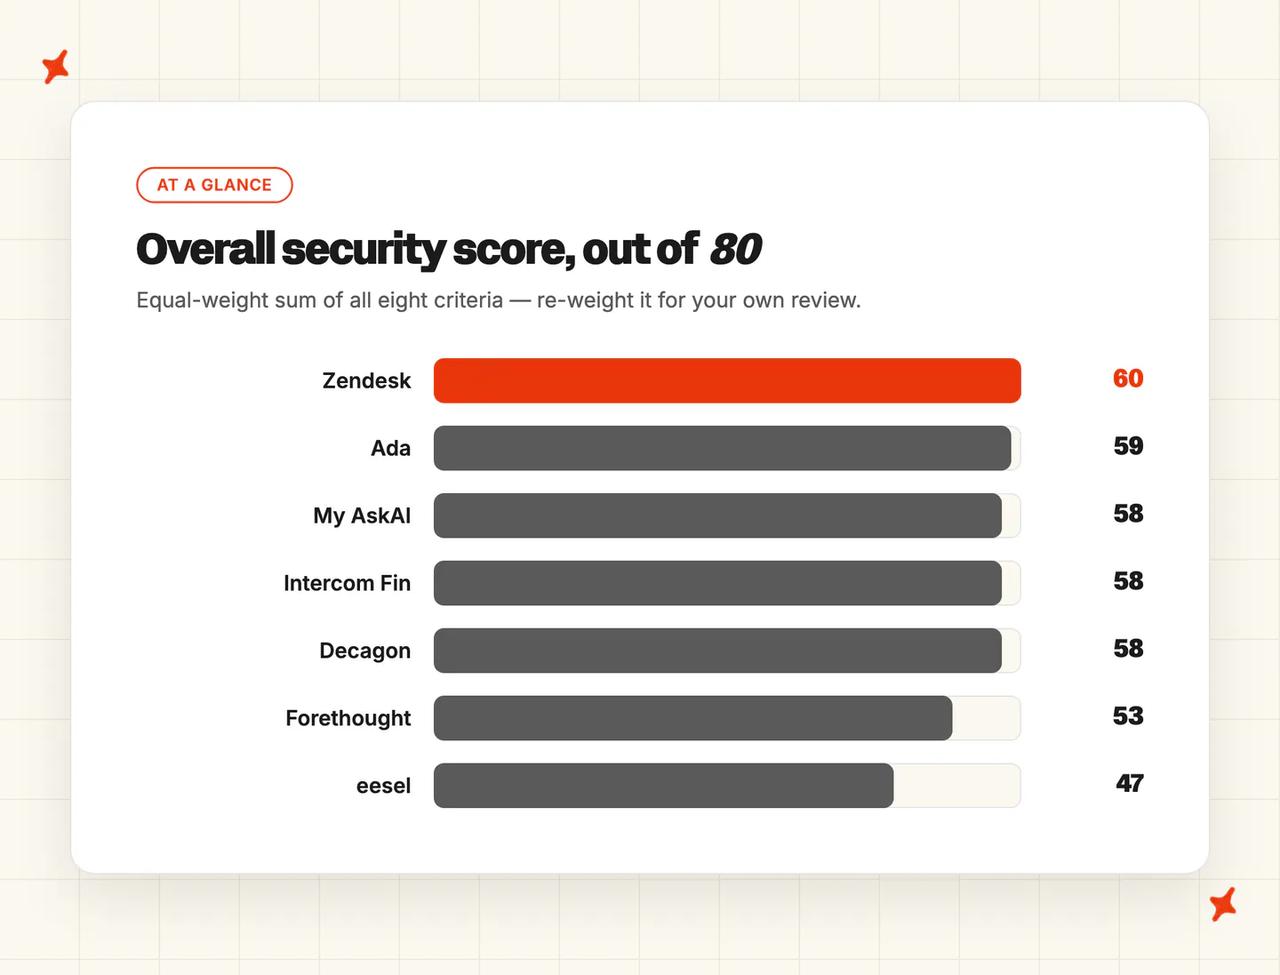
Intercom and Decagon reach it on cert-breadth; My AskAI reaches it on being certified for real, training on nothing, and clearing the review fastest at the most forecastable price. Forethought and eesel round out the list, eesel held back by a SOC 2 that hasn't actually been issued yet.
Where does "compliant AI support" fail?
These are the three failure modes I'd stress-test in the demo. Each one is a place where a tool can look compliant on the homepage and fall apart the moment a reviewer asks a follow-up question.
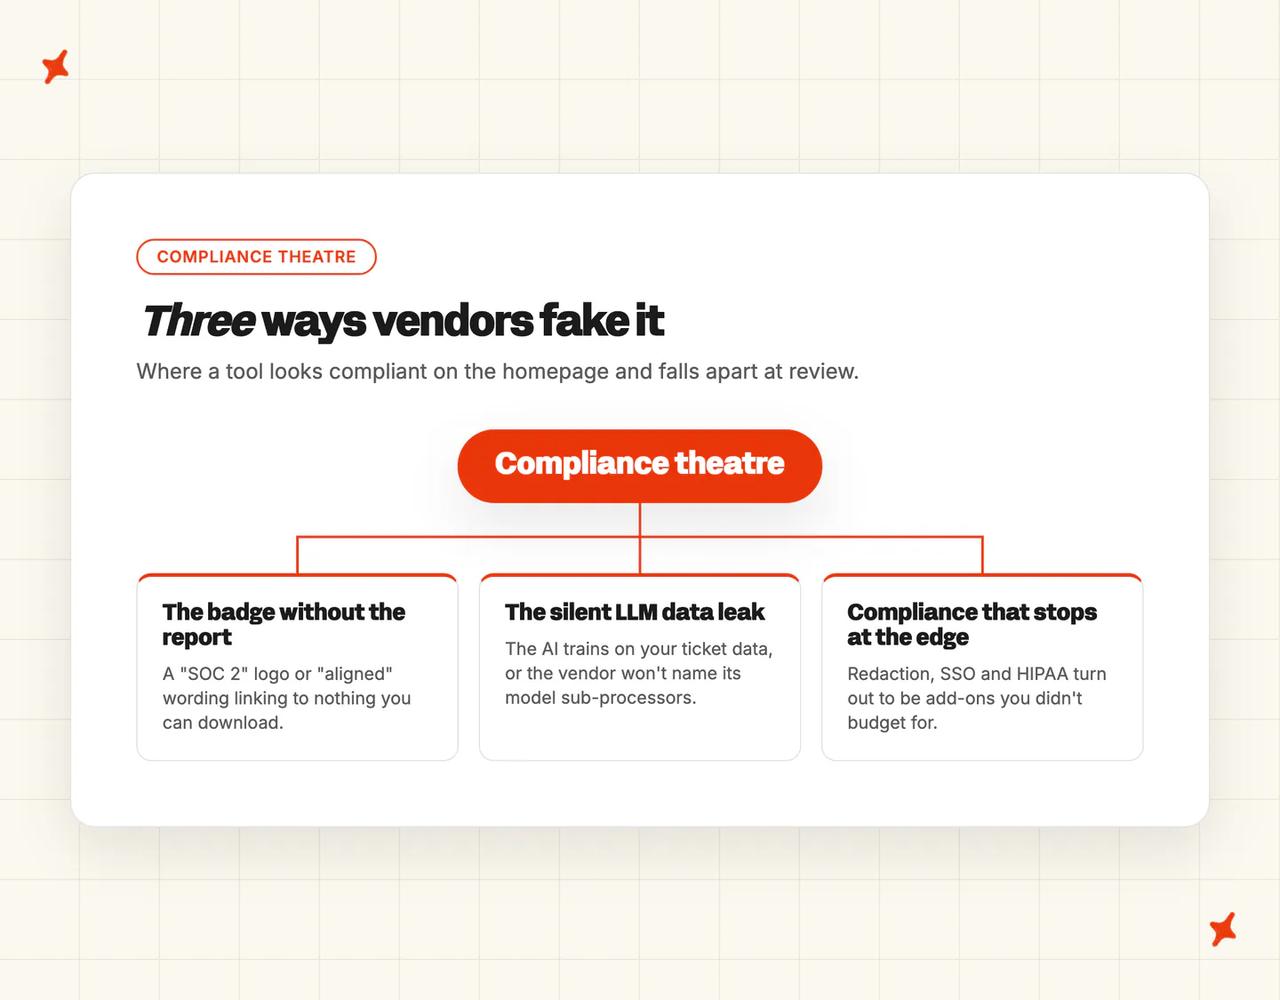
Failure mode 1: the badge without the report
A "SOC 2 Type II" logo that links to nothing you can download, or wording like "SOC 2 aligned" / "compliant with SOC 2" / "certification underway" that a skim-reader takes as certified. The tell is simple: ask for the Type 2 report, the period it covers, and the auditor's name.
eesel AI shows a "SOC 2 Type II" badge in its pricing footer, but its own Vanta trust center reads "SOC2 compliance in-progress", and the only downloadable resource is an engagement letter. The audit is booked; the report doesn't exist yet.
Alhena AI claims SOC 2 Type 2 plus HIPAA and ISO 27001, but those certifications surface only as website footer badges and a blog and LinkedIn announcement, with no trust center, no downloadable report and no auditor named for HIPAA or ISO, so a procurement team can't self-verify any of it. "We can share that later" is the answer that ends a review.
Failure mode 2: the silent LLM data leak
The AI trains on your customers' data, or the vendor won't name its model sub-processors or state its retention terms. Vendors that all say 'SOC 2 certified' still differ sharply here, and the badge can't tell you which.
Intercom trains its own de-identified model on customer data unless you opt out, hold a BAA or run EU-hosted; Zendesk's account-specific models train on that account's data (its OpenAI-powered features run ZDR). Ada, Decagon, eesel and My AskAI don't train models on your data at all.
So "they're SOC 2" tells you nothing here. You have to read the data-use terms, look for a ZDR statement with the model providers, and check for a published sub-processor list.
Failure mode 3: compliance that stops at the platform edge
"Enterprise-grade security" with no residency choice, no published sub-processor list, or the controls you actually need sold as add-ons. None of this is hidden, but a buyer who priced the base plan gets a surprise at review time.
Zendesk offers AI redaction only through its Advanced Data Privacy & Protection add-on (around $50 per agent) and HIPAA only via a paid add-on; eesel gates SSO, HIPAA and BAAs to a $1,000-a-month Enterprise tier. The disqualifier is discovering the control you need is a line item or a "talk to sales" after your champion has already sold the tool internally.
Can My AskAI pass a security review for AI support?
We built My AskAI to sit inside the helpdesk you already run, so it never becomes a new platform holding all your data, and that changes how it clears a security review. On the equal-weight sum we're tied at 58, behind Zendesk and Ada.
How My AskAI handles security and compliance
We're SOC 2 Type II certified, with a real, current attestation (report period 1 July to 30 September 2025), continuously monitored through Secureframe and requestable from our trust center. No "aligned" wording, no "in progress" caveat. We're GDPR-compliant with a DPA and standard contractual clauses, data is AES-256 encrypted at rest and TLS 1.2+ in transit, and each customer runs in an isolated container.
On the question that decides most AI reviews, what happens to your data at the model, our position is the plainest in the set: "Your data is never used to train any AI models: yours, ours, model providers, or any third party's." We publish our sub-processor list (AWS, Azure, Cloudflare, Cohere, Google Cloud and others) on the trust center, and you can read the full security overview before you ever talk to us.
My AskAI connects through scoped OAuth into Zendesk, Intercom, Freshdesk, Gorgias or HubSpot, reading and replying to the tickets already in your helpdesk. There's no new platform accumulating a second copy of your customer data, so the attack surface a reviewer has to reason about stays small, and our technical pass is usually short.
Access is governed by RBAC with audit logs and granular permissions, and data can be deleted from the dashboard directly. When a reviewer asks "how do we know why the AI said what it said", the answer is Echo: you can ask Echo why the agent gave any answer and which knowledge source it used, from inside the dashboard.
Capabilities shipped (out of 6)
| Capability | My AskAI |
|---|---|
| 1. Real, current SOC 2 Type 2 report | ✅ Certified; Jul–Sep 2025 report, Secureframe |
| 2. No training on your data | ✅ Never trains any model |
| 3. PII / PHI redaction before the LLM | ⚠️ Per-customer isolation, not dedicated redaction |
| 4. Residency + sub-processor transparency | ⚠️ Sub-processor list public; residency US-default / EU-on-request, undocumented |
| 5. Access control (SSO/RBAC/audit) | ⚠️ RBAC and audit log shipped; SSO undocumented |
| 6. Adjacent frameworks (ISO/HIPAA/PCI/AIUC-1) | ❌ GDPR only |
Who's using My AskAI for regulated / security-led support?
The clearest proof is GiveCard, a fintech running prepaid cards and disbursements for benefit and aid programs on Zendesk. They put My AskAI on the front line and reached 95% AI resolution at 90% CSAT. As their case study puts it, "For a team handling money for vulnerable people, that's a real act of trust."
Apartment List, an enterprise-scale rental marketplace on Zendesk, runs us at 76% resolution, and a high-volume proprietary-trading platform (fintech, on Intercom, around 105,000 tickets a month) took My AskAI through procurement at scale and runs at 73%. More customer case studies sit alongside these.
How does My AskAI price?
The all-in rate is around $0.10 per ticket, flat and per-ticket, so a 10,000-ticket month is roughly $1,299 on the Scale plan, a number your CFO can forecast a year out. We priced it flat on purpose: it doesn't climb as the AI gets better, the opposite of the per-resolution vendors on this list.
And you can prove it before you pay: the trial is 30 days, all features unlocked, unlimited tickets, no card. A security reviewer can pull the SOC 2 report and walk the data path during that window, so nobody's committing budget before InfoSec has signed off.
Read more in our security overview, the enterprise page for the SLA and custom-dev details, or the pricing page for the full per-ticket breakdown.
Can Intercom Fin pass a security review for AI support?
If the review is about cert breadth, Intercom Fin is the one to beat. It out-certifies most of this list.
How Intercom Fin handles security and compliance
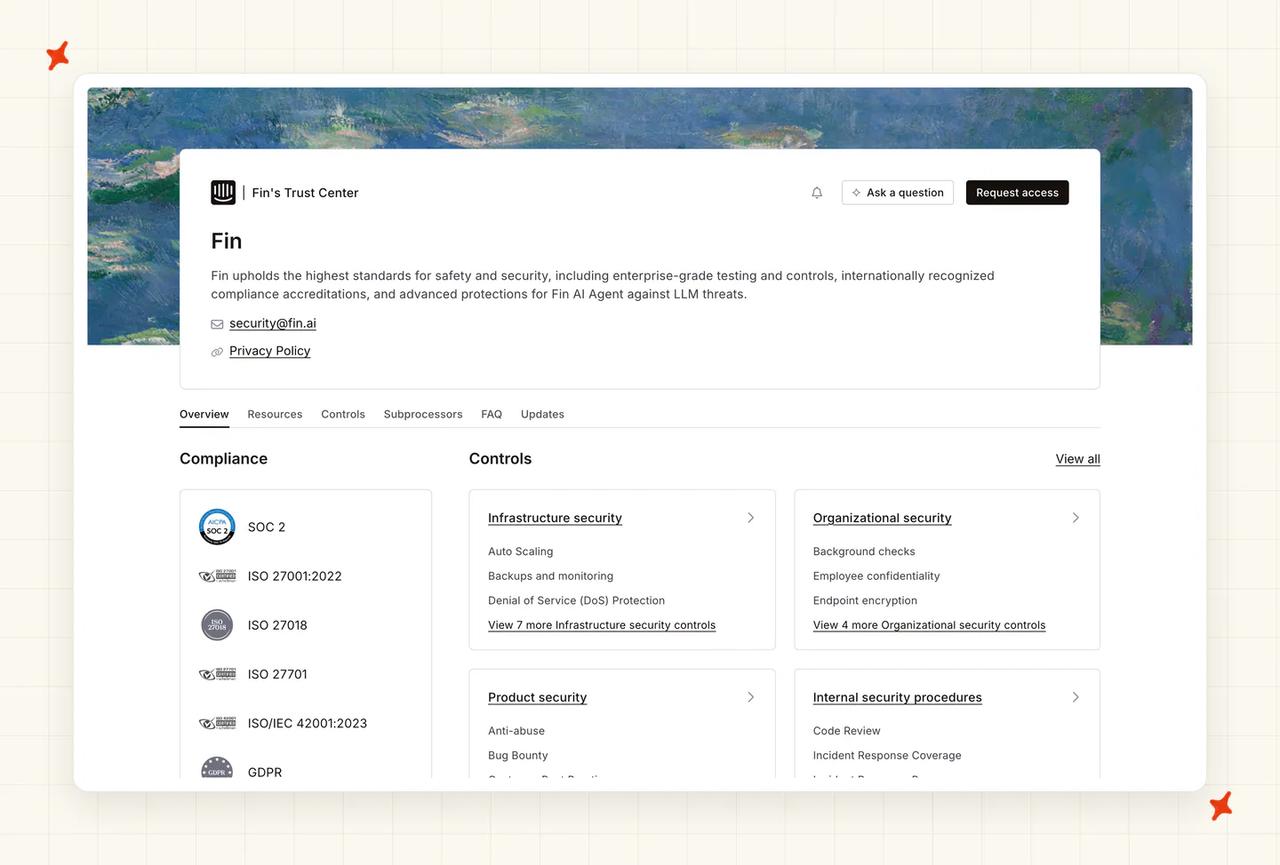
Fin's trust center lists SOC 2 Type II (report under NDA), ISO 27001, 27701 and 27018, ISO 42001, AIUC-1 and HIPAA with a BAA, plus HDS and GDPR/CCPA. That's the widest AI-specific and privacy-management stack here. Data residency is offered across US, EU and Australia, though Intercom's regional hosting docs note it's gated to higher tiers with no in-place migration once you've picked a region.
The catch a reviewer needs to find sits on the data axis: Fin runs zero data retention with its third-party LLM, but it trains its own de-identified (Presidio-scrubbed) Apex model on customer data unless you opt out, hold a BAA, or are EU-hosted. Native redaction covers credit-card (PAN/Luhn) masking only; broader PII redaction relies on a third-party Strac integration, with no native control for it.
SSO is SAML, access is RBAC, and the sub-processor list sits behind a trust-center login. Intercom also publishes a solid guide to evaluating AI-agent security that doubles as a checklist.
Capabilities shipped (out of 6)
| Capability | Intercom Fin |
|---|---|
| 1. Real, current SOC 2 Type 2 report | ✅ Type II, under NDA |
| 2. No training on your data | ⚠️ Trains own de-identified model (opt-out); ZDR with third-party LLM |
| 3. PII / PHI redaction before the LLM | ⚠️ Native card-only; broader PII via third-party Strac |
| 4. Residency + sub-processor transparency | ✅ US/EU/AU (gated tiers); sub-processor list login-gated |
| 5. Access control (SSO/RBAC/audit) | ✅ SAML SSO, RBAC |
| 6. Adjacent frameworks (ISO/HIPAA/PCI/AIUC-1) | ✅ ISO 27001/27701/27018 + ISO 42001 + AIUC-1 + HIPAA/BAA + HDS |
Who's using Intercom Fin for regulated / security-led support?
Intercom cites Anthropic, where Fin is involved in around 96% of conversations, and Lightspeed at roughly 65% resolution. Those are large, security-conscious buyers who've cleared Fin's stack.
How does Intercom Fin price?
Fin bills at $0.99 per resolution on top of Intercom seats. At 10,000 tickets a month and a 75% resolution rate that's around $7,425 a month in Fin fees alone, before seats, and it rises as resolution improves, which is the per-resolution structure I'd model at your real volume before you sign.
Read more on Fin in our complete guide to Intercom Fin, browse the Intercom Fin alternatives roundup, or see the head-to-head in My AskAI vs Intercom Fin.
Can Zendesk pass a security review for AI support?
Zendesk is the enterprise compliance leader in this set, and on the equal-weight sum it comes out on top. Its cert grid is the widest here; the trade-offs are a more complex setup and the least forecastable bill.
How Zendesk handles security and compliance
The Zendesk trust center lists SOC 2 Type II, ISO 27001:2022, 27017, 27018 and 27701, ISO 42001, CSA STAR AI Level 1 and 2 (an industry first), HIPAA via its Advanced Security and Compliance add-on, PCI-DSS Level 1 Service Provider, and FedRAMP LI-SaaS, plus GDPR/CCPA/LGPD. Redaction runs through the Advanced Data Privacy & Protection add-on (around $50 per agent): AI redaction suggestions, PCI redaction, call-transcription PII redaction, BYOK and role-based masking.
On the data axis, Zendesk's account-specific models train on that account's data, while its OpenAI-powered features run ZDR. SSO/SAML, RBAC and audit logs come at the Enterprise tier, residency spans US, EU and APAC (plus AU/JP via a Data Center Location add-on), and the sub-processor list is public.
Capabilities shipped (out of 6)
| Capability | Zendesk |
|---|---|
| 1. Real, current SOC 2 Type 2 report | ✅ Type II, under NDA |
| 2. No training on your data | ⚠️ Account-specific models train on your data; OpenAI features ZDR |
| 3. PII / PHI redaction before the LLM | ✅ ADPP add-on (paid) |
| 4. Residency + sub-processor transparency | ✅ US/EU/APAC + AU/JP add-on; public sub-processor list |
| 5. Access control (SSO/RBAC/audit) | ✅ SSO, RBAC, audit (Enterprise) |
| 6. Adjacent frameworks (ISO/HIPAA/PCI/AIUC-1) | ✅ ISO 27001/42001 + CSA STAR AI + HIPAA add-on + PCI L1 + FedRAMP |
Who's using Zendesk for regulated / security-led support?
Zendesk cites Siemens Financial Services, a regulated-finance operation running AI agents that auto-send invoices, a workload that only ships after a serious review.
How does Zendesk price?
Zendesk AI bills per automated resolution on top of Zendesk Suite seats, and at 10,000 tickets a month around $11,250 is a representative monthly figure, before you add ADPP, HIPAA or the residency add-on. It's the most capable grid on the list and the least forecastable bill, so I'd price the add-ons in from the start, because it's lightest for teams already standardized on Zendesk.
Read more on Zendesk in our complete guide to Zendesk AI, browse the Zendesk AI alternatives roundup, or compare directly in My AskAI vs Zendesk AI.
Can Forethought pass a security review for AI support?
Forethought is a strong mid-enterprise pick whose standout is data minimization done by default, with no bolt-on required.
How Forethought handles security and compliance
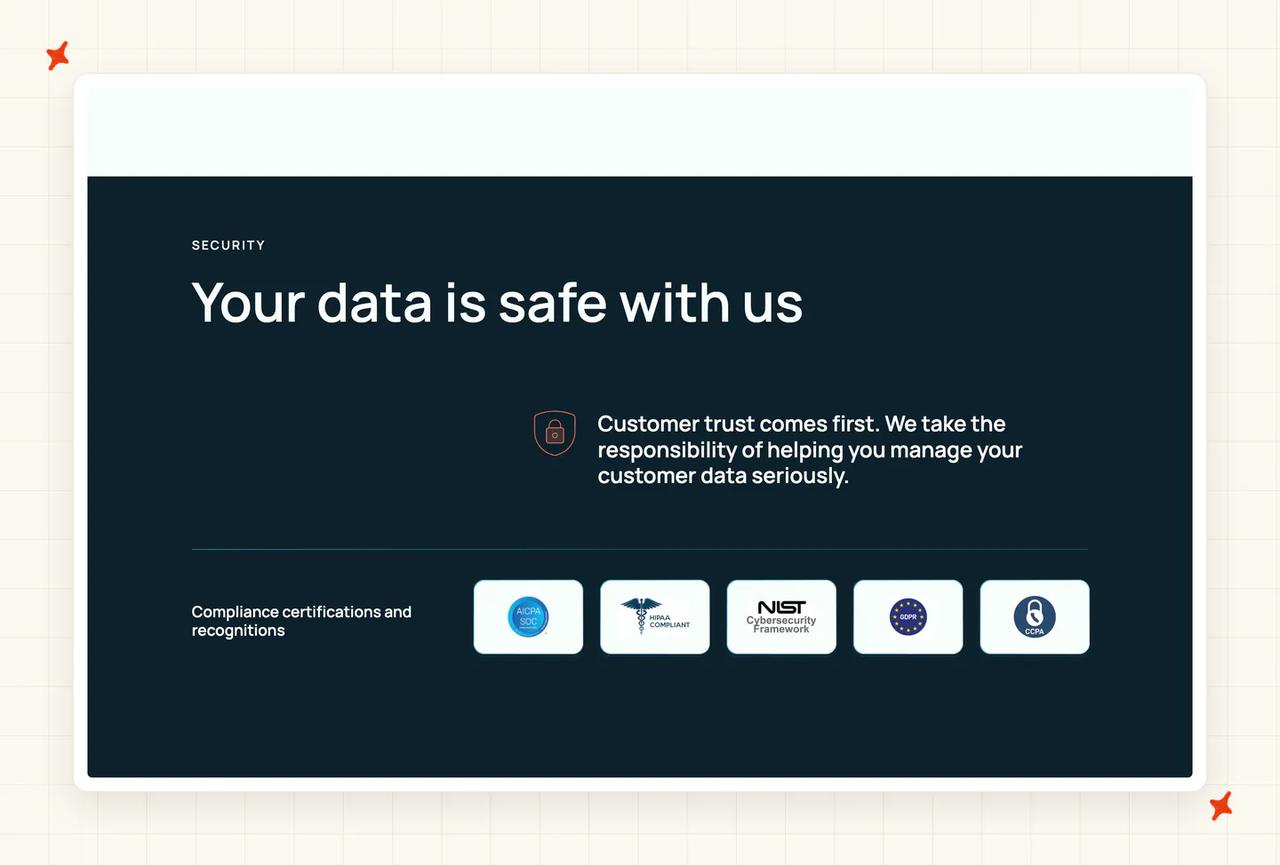
Forethought holds SOC 2 Type II (annual, with NIST 800-53 alignment), states it's compliant with ISO 27001, and carries HIPAA plus GDPR/CCPA and NIST CSF, all documented on its security page. Its differentiator is redaction: it's the first helpdesk-AI vendor to redact all PII, PHI and financial data by default on ingestion, with originals deleted within 24 hours on a best-effort basis.
It doesn't train shared models on your data. The gaps a reviewer will note are that residency and the sub-processor list aren't publicly documented (the trust center is gated), and its FedRAMP application isn't certified.
Capabilities shipped (out of 6)
| Capability | Forethought |
|---|---|
| 1. Real, current SOC 2 Type 2 report | ✅ Type II, annual |
| 2. No training on your data | ✅ No shared-model training |
| 3. PII / PHI redaction before the LLM | ✅ Default PII/PHI/financial redaction on ingestion |
| 4. Residency + sub-processor transparency | ⚠️ Residency undocumented; sub-processor list gated |
| 5. Access control (SSO/RBAC/audit) | ⚠️ RBAC; SSO not detailed publicly |
| 6. Adjacent frameworks (ISO/HIPAA/PCI/AIUC-1) | ✅ ISO 27001 + HIPAA + NIST (no ISO 42001/AIUC-1/PCI) |
Who's using Forethought for regulated / security-led support?
Forethought publicly cites Upwork (around 50% faster resolution), along with Instacart, Grammarly and Datadog, all large buyers with real security functions. One caveat worth surfacing for a customer-facing deployment: word-on-the-street (and consumer reviews) flag conversational loops and hard escalation, so test the hand-off path in your own demo.
How does Forethought price?
Forethought sells on an annual contract with opaque, sales-gated pricing and a 30 to 90 day implementation that leans on a CSM, with no self-serve path. For a review that arrives mid-trial, I'd flag that timeline as the real friction: you can't quickly stand it up to test before the security conversation.
Read more on Forethought in our complete guide to Forethought or browse the Forethought alternatives roundup.
Can Ada pass a security review for AI support?
Ada is a well-documented enterprise agent whose one notable omission is ISO 27001; it bet on the newer AI-specific AIUC-1 instead.
How Ada handles security and compliance
Ada runs a full public Trust Center listing SOC 2 Type II and SOC 3 (report period Oct 2023 to Sep 2024), HIPAA, a PCI AOC, AIUC-1 (the first AI CS platform to earn it), and GDPR/CCPA/CPRA/PIPEDA, with downloadable pen-test and AI-security reports, data-flow diagrams and network diagrams, and a SecurityScorecard A. What it doesn't hold is ISO 27001 or ISO 42001. On data, customer data never trains models and Ada publishes its ZDR agreements with every LLM provider, the transparency leader here.
It offers built-in configurable PII/PHI redaction, RBAC with MFA, audit logging and FINRA/SEC-grade conversation logging, contractual (rather than tier-gated) data residency, and a public sub-processor list. More detail sits on its trust page.
Capabilities shipped (out of 6)
| Capability | Ada |
|---|---|
| 1. Real, current SOC 2 Type 2 report | ✅ Type II + SOC 3, dated report |
| 2. No training on your data | ✅ No training; publishes ZDR agreements |
| 3. PII / PHI redaction before the LLM | ✅ Built-in, configurable |
| 4. Residency + sub-processor transparency | ✅ Contractual residency; public sub-processor page |
| 5. Access control (SSO/RBAC/audit) | ✅ RBAC, MFA, audit, FINRA/SEC logging |
| 6. Adjacent frameworks (ISO/HIPAA/PCI/AIUC-1) | ✅ HIPAA + PCI AOC + AIUC-1 + SOC 3 (no ISO 27001) |
Who's using Ada for regulated / security-led support?
Ada cites Wealthsimple, a regulated fintech, and Verizon's BlueJeans at around 72% containment, both buyers whose reviews are not light.
How does Ada price?
Ada isn't self-serve; expect an 8 to 16 week implementation and opaque, volume-banded pricing (Vendr's median lands around $73,500 a year, roughly $6,000 a month), and Ada's own pricing page no longer states a conversation-volume qualification bar. You can verify the security setup yourself from the trust center during the trial, though you can't quickly test the product before the review.
Read more on Ada in our complete guide to Ada or browse the Ada alternatives roundup.
Can Decagon pass a security review for AI support?
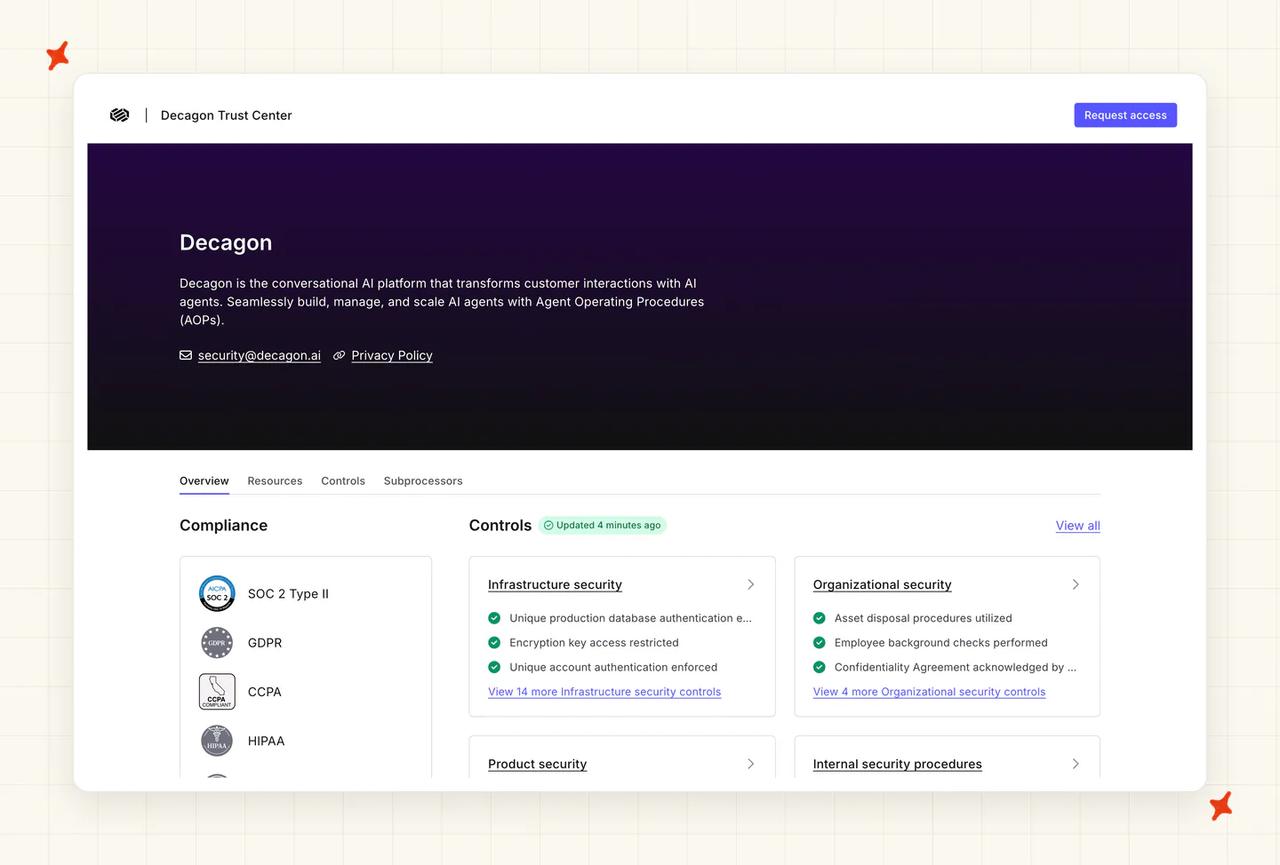
Decagon is an agent-native enterprise vendor whose trust center lists the most documents in this set, though every one of them sits behind a request-access approval.
How Decagon handles security and compliance
Decagon's trust center (on Vanta) lists SOC 2 Type II reports (covering Apr to Oct 2025 and Oct 2024 to Apr 2025), an ISO 27001:2022 certificate issued 22 January 2026, HIPAA with BAAs on enterprise, a PCI DSS 4.0.1 badge, EU AI Act coverage and GDPR/CCPA. Data is AES-256/TLS 1.2+, redaction runs through Google DLP, and it holds zero-day retention with all LLM providers, so nothing trains on your data.
Access is SSO (Okta/Entra), RBAC and tamper-protected audit logs, and the sub-processor list is published. The friction here is commercial, and the technical side is fine: it's sales-gated with no self-serve pricing, enterprise-only, and carries a qualification bar around 300,000 conversations.
Capabilities shipped (out of 6)
| Capability | Decagon |
|---|---|
| 1. Real, current SOC 2 Type 2 report | ✅ Two consecutive Type II reports, released on request |
| 2. No training on your data | ✅ Zero-day retention, no training |
| 3. PII / PHI redaction before the LLM | ✅ Google DLP redaction |
| 4. Residency + sub-processor transparency | ✅ Published sub-processors; multi-region |
| 5. Access control (SSO/RBAC/audit) | ✅ SSO Okta/Entra, RBAC, tamper-proof audit |
| 6. Adjacent frameworks (ISO/HIPAA/PCI/AIUC-1) | ✅ ISO 27001 + HIPAA/BAA + PCI badge + EU AI Act (no ISO 42001/AIUC-1) |
Who's using Decagon for regulated / security-led support?
Decagon cites Rippling, where it drove a 32% increase in deflection, and ClassPass at a reported 95% cost reduction, both enterprise buyers with real diligence.
How does Decagon price?
Pricing is opaque and sales-gated, enterprise-only, with no published rate card and the same ~300,000-conversation qualification bar. The trust center is the easiest to verify in the set; pull the reports on day one. The commercial process is the slowest to start.
Read more on Decagon in our complete guide to Decagon or browse the Decagon alternatives roundup.
Can eesel pass a security review for AI support?
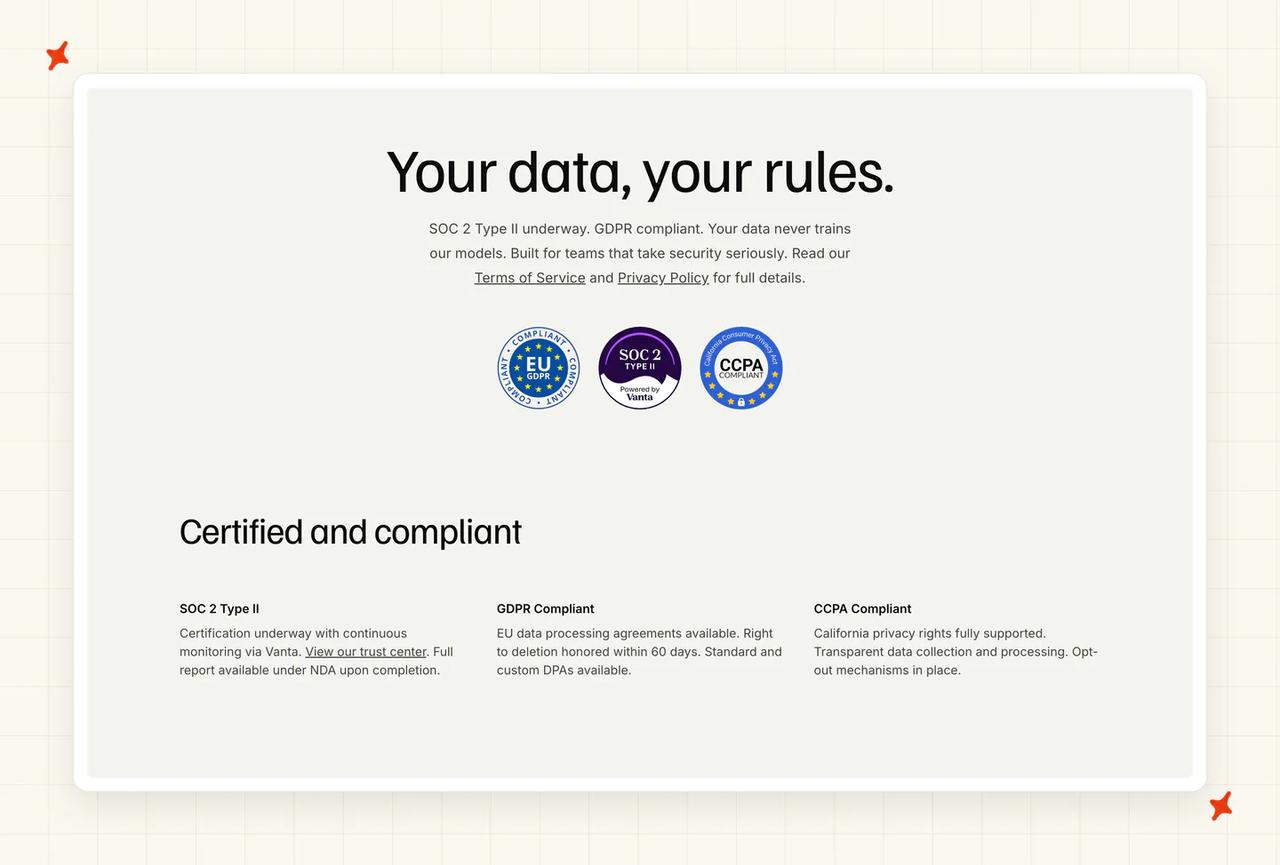
eesel is a real, self-serve tool with 2,000+ customers, but its SOC 2 status is exactly the 'badge versus report' gap this post is about.
How eesel handles security and compliance
eesel's live Vanta trust center reads "SOC2 compliance in-progress", and the only downloadable resource is an engagement letter. The audit is engaged; no report has been issued yet. The "SOC 2 Type II" badge in its pricing footer overstates that.
It holds GDPR/CCPA with an enterprise-only DPA (via Common Paper), offers EU data residency on request (US-default on AWS), and strips PII (cards, emails, SSNs, API keys and names) before sending to the AI providers, with contractual no-training and 60-day deletion. Data is AES-256/TLS.
The controls a reviewer usually needs are gated: SSO, HIPAA and BAAs all sit on the $1,000-a-month Enterprise tier. RBAC is least-privilege, and the public sub-processor list is partial (AWS, Pinecone, OpenAI, Anthropic, Google). It's plug-and-play on top of your existing helpdesk, which means you pay for both.
Capabilities shipped (out of 6)
| Capability | eesel |
|---|---|
| 1. Real, current SOC 2 Type 2 report | ❌ In-progress; engagement letter only |
| 2. No training on your data | ✅ Contractual no-training |
| 3. PII / PHI redaction before the LLM | ✅ Strips PII before AI providers |
| 4. Residency + sub-processor transparency | ✅ EU on request; partial public sub-processor list |
| 5. Access control (SSO/RBAC/audit) | ⚠️ SSO Enterprise-gated; RBAC shipped |
| 6. Adjacent frameworks (ISO/HIPAA/PCI/AIUC-1) | ⚠️ GDPR/CCPA; HIPAA Enterprise-gated; no ISO |
Who's using eesel for regulated / security-led support?
eesel publishes customer logos, but no durable, security-relevant named case study for a post like this. For a security-led buyer, I'd say the in-progress SOC 2 is the thing to resolve before shortlisting it, whoever else uses it.
How does eesel price?
eesel is tiered with pay-as-you-go usage on top, and because it layers on your existing helpdesk you're effectively paying twice for the same tickets. The self-serve setup is fast, but I'd note the SSO/HIPAA/BAA controls a mid-market review needs only appear at the $1,000-a-month Enterprise tier.
Read more on eesel in our complete guide to eesel, browse the eesel alternatives roundup, or see the head-to-head in My AskAI vs eesel.
What does a failed security review actually cost you? (worked example)
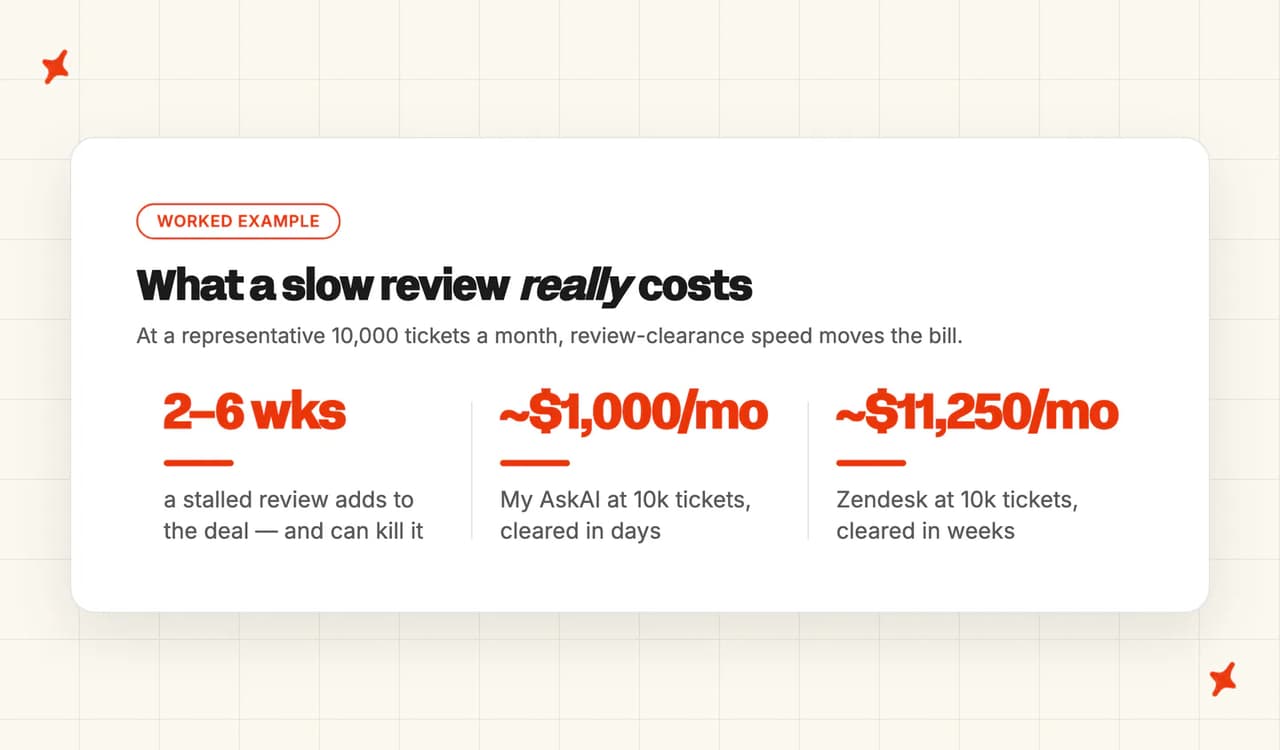
A slow or failed review costs you well beyond the per-ticket rate. In my experience the reviewer arrives two to four weeks into the trial, after your champion and economic buyer have already said yes, and adds an asynchronous 2 to 6 week cycle on top of the 2 to 4 weeks of procurement already in motion.
If the vendor then fails the review, you re-procure: the eval hours your team already spent are sunk, and the rollout slips by however long it takes to find and re-test a replacement. Every week of slip is another week the ticket tail the tool was meant to fix stays manual.
At a representative 10,000 tickets a month, review-clearance speed changes the real cost of each option:
| Scenario | Monthly cost (10k tickets) | Time to clear review | Notes |
|---|---|---|---|
| Failed review → re-procure | Sunk eval + weeks of deal slip | Restart | The outcome every other row is trying to avoid |
| My AskAI ($0.10/ticket) | ~$1,299, forecastable | Days | Certified, self-serve, helpdesk-native, scoped OAuth |
| Intercom Fin ($0.99/resolution) | ~$7,425 + seats | Days to weeks | Self-serve to test; cert grid clears fast; bill climbs with resolution |
| Zendesk (per-resolution + add-ons) | ~$11,250 + add-ons | Weeks | Redaction/HIPAA are paid add-ons to price in |
| Ada (opaque, enterprise) | ~$6,000 | Weeks | Verify security fast; but 8 to 16 week rollout before you can test |
Certified, self-serve and helpdesk-native vendors clear in days; the sales-gated enterprise ones add weeks before you can even start testing. When a review lands mid-trial, the vendor you can stand up and verify this week is the one that protects the deal.
So which SOC 2-compliant AI customer service tool is best?
There isn't one winner; 'best' depends on what your review gates on. Re-weight the scoreboard for your own priorities before you treat any total as a verdict.
If your buyer is regulated and the review demands HIPAA, ISO 27001 or PCI on top of SOC 2, go to Zendesk (the broadest verified grid, top of the equal-weight sum) or Intercom Fin (the deepest AI-specific and privacy stack). Want an enterprise agent whose security setup you can verify yourself before a sales call? Decagon lists two consecutive Type II reports you can request, and Ada publishes pen-test reports and its ZDR agreements.
My AskAI is the pick when you need a vendor that's certified, trains on nothing, clears the review this week because it lives inside your helpdesk on scoped OAuth, and bills a flat, forecastable per-ticket rate. If HIPAA or ISO 27001 is on your list, though, you'll want a vendor that carries them.
SOC 2 is the stage gate scale-ups quickly need once mid-market security reviewers arrive; the frameworks beyond it are a real requirement for some buyers and overkill for others.
Whatever you shortlist, run the review like a reviewer would. Ask for the Type 2 report, the period it covers and the auditor's name on day one; start the AI in draft or copilot mode so it's writing internal notes before it replies to a customer; and read the sub-processor list before go-live, well ahead of launch day. A vendor that answers all three cleanly is one your security team will bless.
You can pull our SOC 2 report and walk the whole data path yourself at our trust center or read the security overview, and the 30-day trial runs all features on unlimited tickets with no card so InfoSec can sign off before you commit a penny.
FAQs
How do I make sure my AI customer support is GDPR and SOC 2 compliant?
Check the six things a real review gates on: a current SOC 2 Type 2 report (not "aligned" or "in progress"), no training on your data, PII redaction before the LLM, published residency and sub-processor transparency with a DPA, access control (SSO/RBAC/audit), and any adjacent frameworks your industry needs. GDPR compliance specifically means a signed DPA, standard contractual clauses where data leaves the region, and a current sub-processor list your DPO can assess. The shortcut that catches most fakes: ask for the Type 2 report and the auditor's name before you go further.
Is "SOC 2 aligned" or "SOC 2 in progress" the same as being SOC 2 compliant?
No. "Aligned", "in progress" or "compliant with SOC 2" means the vendor hasn't been issued a report you can read. A real Type 2 attestation covers a defined period of operating effectiveness, is signed by a named auditor, and is requestable under NDA, ideally self-serve from a live trust center.
On this list, eesel's trust center reads "SOC2 compliance in-progress" with only an engagement letter to download, and Alhena's claims live in blog and LinkedIn posts with no report behind them. Both show the badge with no attestation behind it, and that gap is exactly where a security review stalls.
What happens to my customers' data when it's sent to the AI's language model?
That depends entirely on the vendor. It's the axis a generic SOC 2 badge won't tell you about. Three questions decide it: does the vendor train its own models on your data, do the third-party model providers retain or train on it, and what's the retention window?
On this list, Intercom trains its own de-identified model unless you opt out, and Zendesk's account-specific models train on that account's data, while Ada, Decagon, eesel and My AskAI don't train on your data at all. Look for contractual no-training plus zero-data-retention agreements with the model providers.
Do I need HIPAA as well as SOC 2 for AI customer support?
Only if protected health information is in scope for the tickets the AI will handle. If you're in healthcare or handling PHI, you need HIPAA and a BAA on top of SOC 2, which points you to Intercom Fin, Zendesk, Forethought, Ada or Decagon on this list.
My AskAI holds SOC 2 Type II and GDPR, so if PHI is in scope I'd steer you to one of the vendors that carries HIPAA and save your review's time. For the large majority of SaaS and ecommerce buyers, SOC 2 Type II plus GDPR is the bar.
Can AI customer support be hosted in the EU or UK for data residency?
Several of these vendors offer it, with different terms. Zendesk offers selectable US/EU/APAC regions, Intercom Fin offers US/EU/AU gated to higher tiers with no in-place migration, Ada provides contractual residency, and eesel offers EU residency on request against a US default.
My AskAI defaults to US hosting with EU on request as a manual conversation. If EU or UK residency is a hard requirement, I'd confirm it in writing during the trial and not assume a region toggle exists.
How do I get a vendor's SOC 2 Type 2 report?
From the vendor's trust center: some let you download it self-serve, others release it under NDA. Ada lets you pull the reports directly from its trust center, Decagon lists its reports behind a request-access approval, My AskAI provides its report from its trust center, and Intercom, Zendesk and Forethought release theirs under NDA. If a vendor can't produce a report at all and instead points you to a badge or an "in progress" page, that's your answer on where their SOC 2 actually stands.
Does adding AI to my helpdesk create a new security risk?
It can, and the size of the risk depends on the architecture. A tool that stands up a new platform holding a second copy of all your customer data widens the attack surface your reviewer has to assess.
A tool that connects through scoped OAuth into your existing helpdesk, reading and replying to the tickets already there without a separate data store, keeps the surface small and the review short. We built My AskAI the second way, which is a large part of why our technical pass is usually quick.
Which AI customer support tool clears a security review fastest?
The one that's already certified, self-serve enough to test during the trial, and has the smallest attack surface. Sales-gated enterprise vendors like Ada and Decagon give you verifiable trust centers but multi-week implementations before you can even test the product. A certified, helpdesk-native, self-serve tool clears in days because the reviewer is assessing scoped access to a platform you already run, with no brand-new system holding your data.
Which AI customer service tools meet both SOC 2 and ISO 27001?
Four of the seven here hold both. Zendesk carries SOC 2 Type II with the full ISO 27001 family and ISO 42001, Intercom Fin carries SOC 2 Type II with ISO 27001, 27701, 27018 and 42001, Decagon holds SOC 2 Type II with an ISO 27001:2022 certificate issued in January 2026, and Forethought states ISO 27001 alongside its annual SOC 2 Type II. Ada is the notable miss, with a strong trust center covering SOC 2 Type II, SOC 3, HIPAA and AIUC-1, but no ISO 27001 at all. My AskAI and eesel do not hold it either, so if your review names ISO 27001 as a hard requirement, the shortlist is those four.